In cybersecurity there is the principle of least privilege — a user or process should have only the access it needs to do its job. Privacy law has a close cousin: data minimization. You should hold only the personal data genuinely necessary to provide your service, and keep it no longer than you need.
In practice, minimization works in three directions: collect less, retain less, and expose less. This guide covers what the regulations require and how Databunker Pro helps you do all three.
What data minimization means
GDPR Article 5 sets it out directly: personal data shall be "(c) adequate, relevant and limited to what is necessary in relation to the purposes for which they are processed" — and "(e) kept in a form which permits identification… for no longer than is necessary." Clause (c) is minimization; clause (e) is storage limitation, its retention twin.
It isn’t only a European idea:
- CPRA (California, 2020) requires that collection, use, retention, and sharing be “reasonably necessary and proportionate” to the disclosed purpose — and that retention periods be stated.
- HIPAA’s minimum necessary rule says the same for health data.
Minimization is also a pillar of Article 25 — data protection by design and by default: build systems that default to the least data.
Why it matters
Minimization means you can’t keep data forever “just in case.” When a trial lapses or a customer leaves, their records should go.
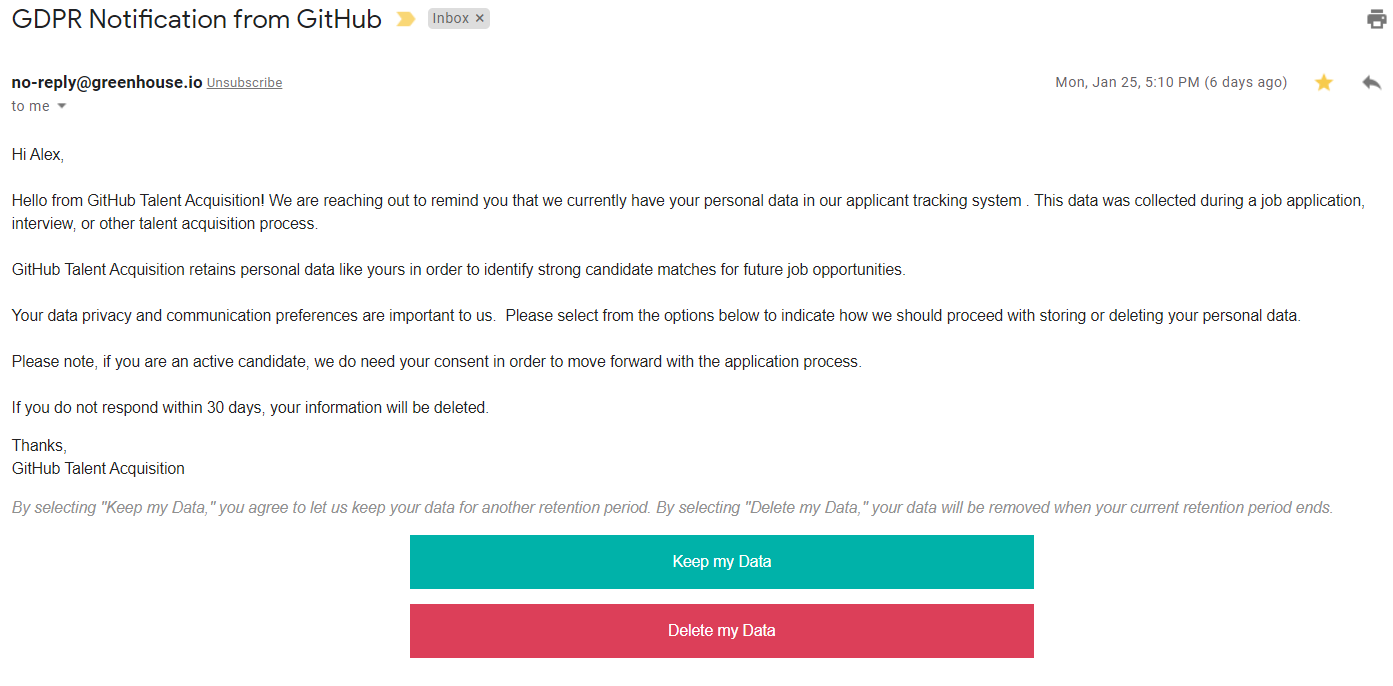
The email above is GitHub telling a job candidate it will delete their data in 30 days unless they press “Keep my data.” That is storage limitation in action — and notice GitHub didn’t wait for a forget-me request; it began deletion proactively. You should too. The payoff is concrete: less data means a smaller breach blast radius, lower storage and compliance cost, and fewer systems in audit scope.
How Databunker Pro helps you minimize
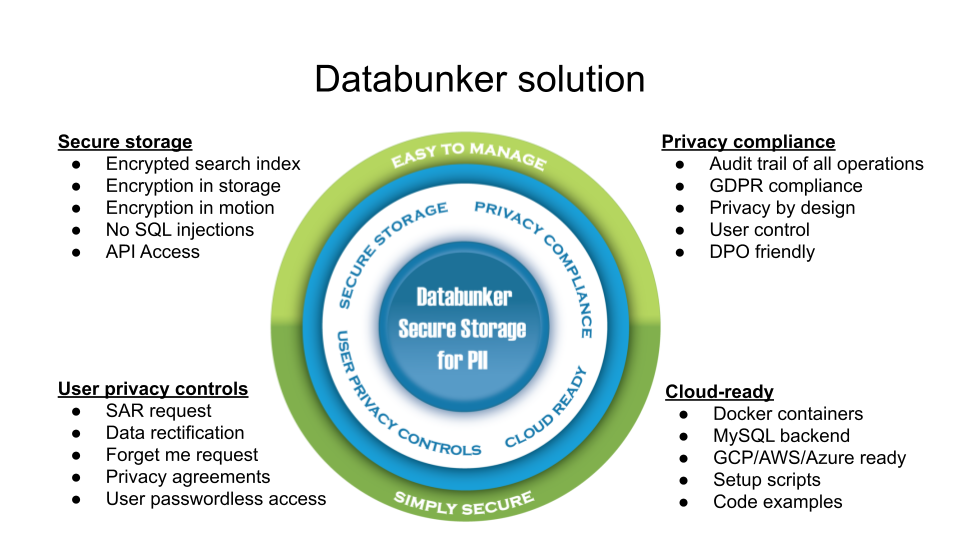
Databunker Pro is a secure vault for customer records, built so minimization is the default rather than a project.
Expose less — tokenize your PII
Tokenization is a recognised pseudonymization technique. Store personal data in the vault, and your application database, logs, and analytics keep only opaque tokens. Your operational systems then hold the bare minimum — non-identifying references — so even an SQL-injection dump exposes no real personal data. That is data minimization by design. See PII tokenization and pseudonymization vs anonymization.
Retain less — expire records automatically
Set a retention window when you create a record, and Databunker enforces it for you:
|
|
slidingtime extends the window on activity; finaltime is an absolute cap. Together they turn your written retention policy into something the vault enforces on its own.
Access less — reveal only what’s needed
Minimization includes who can see data. Conditional role-based access control (CRBAC) and field masking ensure each role sees only the fields it needs — a support agent might see an email but not payment details — and bulk access is default-deny and audited.
Summary
Data minimization is collect less, retain less, expose less. Databunker Pro delivers all three: tokenize PII so your systems hold non-identifying references, set retention windows that auto-expire stale records, and mask fields by role. Article 5 stops being a policy document and becomes how your system behaves. Pair it with the GDPR user request workflow to automate erasure end to end.
Frequently asked questions
What is data minimization? Collecting and keeping only the personal data necessary for a stated purpose — GDPR Article 5(1)(c).
Data minimization vs. storage limitation? Minimization limits what you collect; storage limitation (Article 5(1)(e)) limits how long you keep it. You need both.
Is pseudonymization the same as data minimization? No — pseudonymization, such as tokenization, is a technique that supports minimization by reducing the identifying data your systems hold.
How do I start? Audit what you collect, drop what you don’t need, set retention windows, and tokenize the PII that remains.